The CodeKits notebook
Ideas into working code.
Practical tutorials, project walkthroughs and development notes. Explore the code, understand the structure, and build something of your own.
12 articles · Newest first
Security
Hashing, encoding and signatures for app developers
Distinguish Base64, file hashes, encryption and signatures with small Node tests, then choose the right tool for application security.
· 5 min read
Security
Your first-hour server incident command sheet
Record a suspected Ubuntu server incident, preserve bounded diagnostic evidence and plan containment without destroying useful context.
· 5 min read
Security
Keep production configuration out of public code
Separate browser, build and runtime configuration, protect environment files, and diagnose missing settings without printing private values.
· 6 min read
Security
Review your Ubuntu server's exposed services
Compare Ubuntu listeners, host firewall rules and provider controls with the services you intended to publish, without broad scanning.
· 5 min read
Security
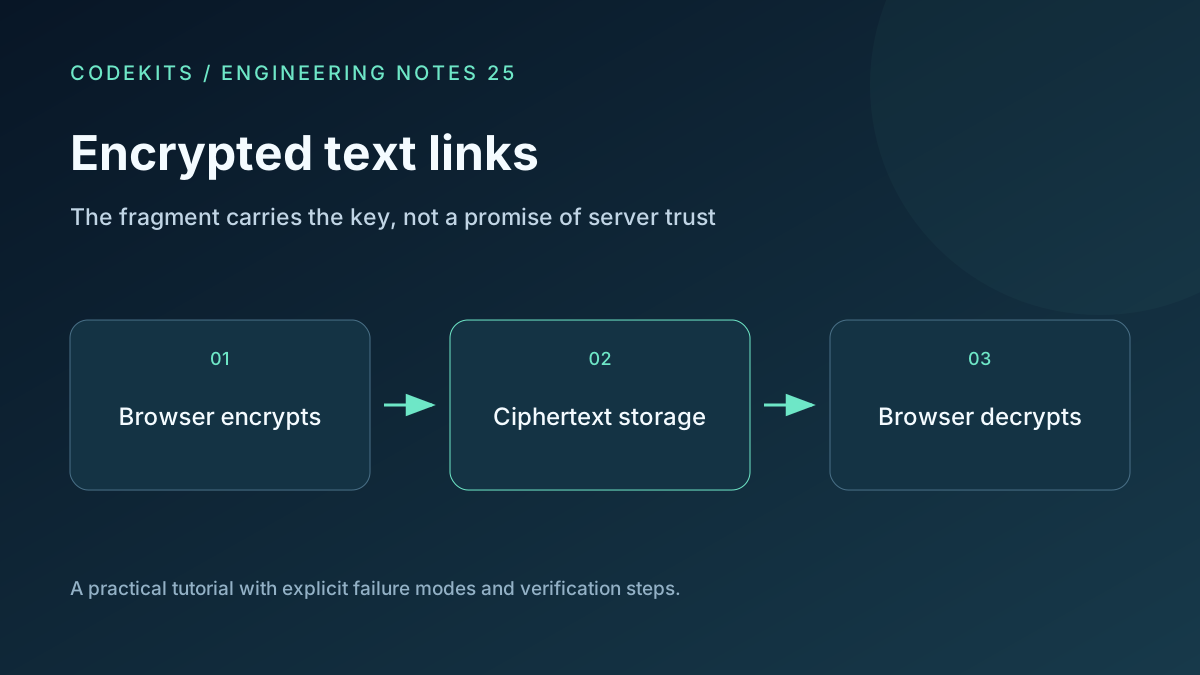
Build browser-encrypted one-time text links
Encrypt text in the browser, put the random key in a URL fragment, and combine ciphertext storage with explicit one-time retrieval and trust limits.
· 4 min read
Security
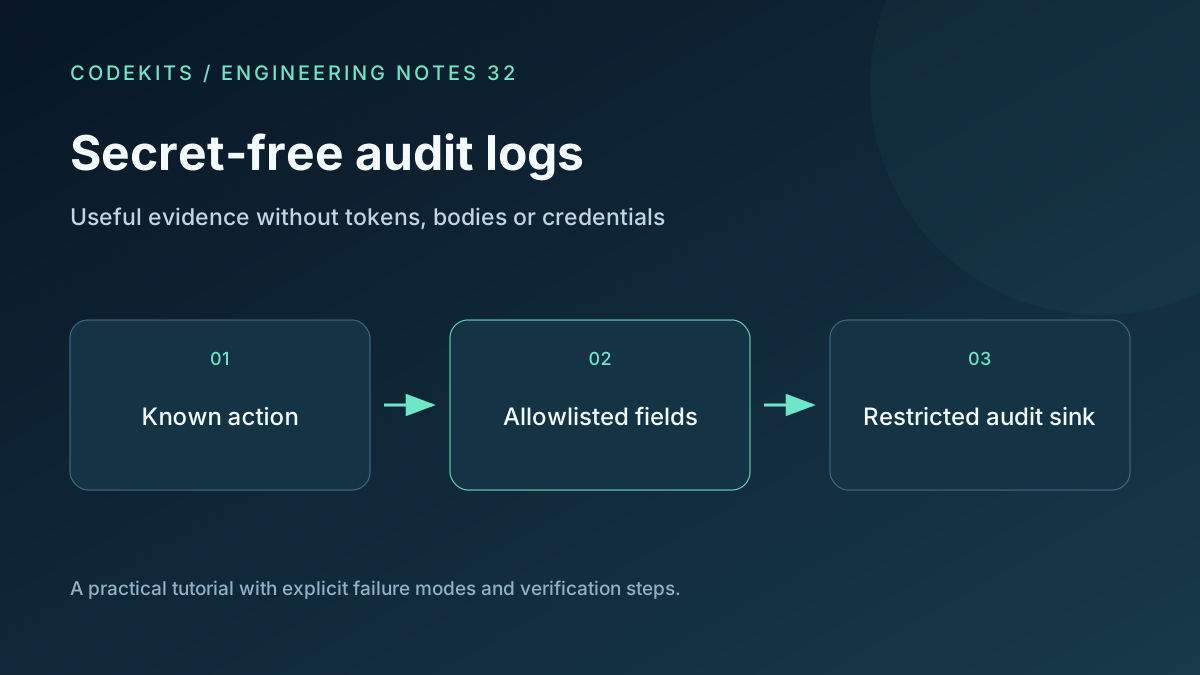
Create useful audit logs without recording secrets
Create structured audit events with allowlisted actions and internal identifiers, while excluding tokens, credentials, request bodies and private messages.
· 4 min read
Security
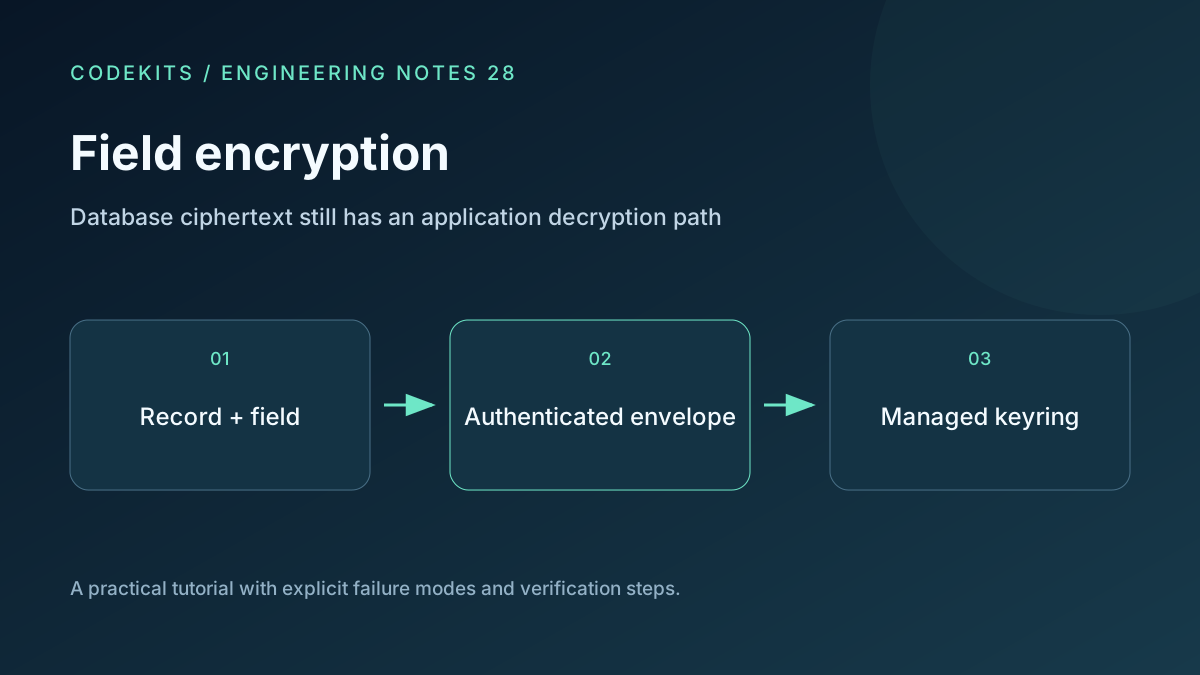
Encrypt sensitive MySQL fields in Node.js
Use authenticated field encryption with record-bound context, versioned envelopes and managed keys while keeping database and application threats distinct.
· 4 min read
Security
Make read-once links race-safe with MySQL
Serialize one-time secret consumption with an InnoDB row lock, commit before responding, and document why at-most-once retrieval cannot guarantee delivery.
· 4 min read
Security
Protect admin APIs and private downloads
Enforce authentication and object-level authorization at every server entry point, with negative tests for direct API calls and private-file access.
· 4 min read
Security
Revoke temporary links and understand the limits
Implement server-side link revocation with owner-scoped updates, explicit cache policy and a clear distinction between future grants and existing copies.
· 4 min read
Security
Rotate encryption keys without losing records
Introduce a new write key without breaking old ciphertext, migrate records with conflict checks, and prove historical backups remain recoverable.
· 4 min read
Security
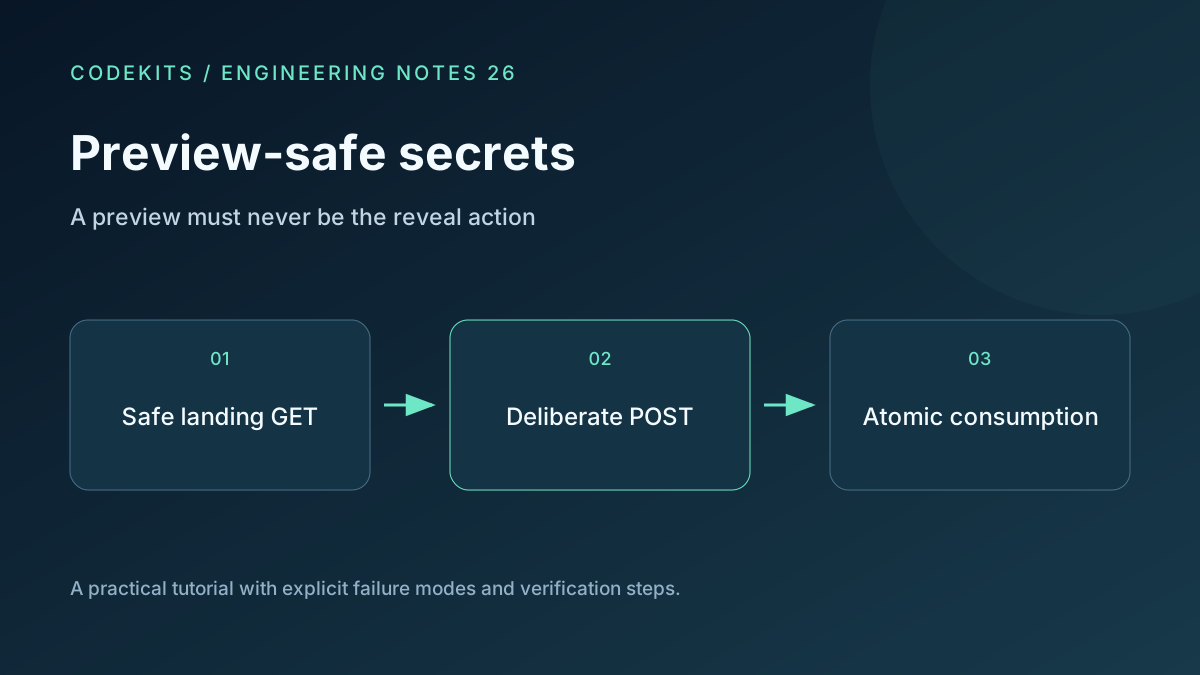
Stop link previews from consuming one-time secrets
Keep landing-page GET and HEAD requests non-consuming, require an explicit reveal POST, and avoid mistaking preview protection for recipient authentication.
· 4 min read